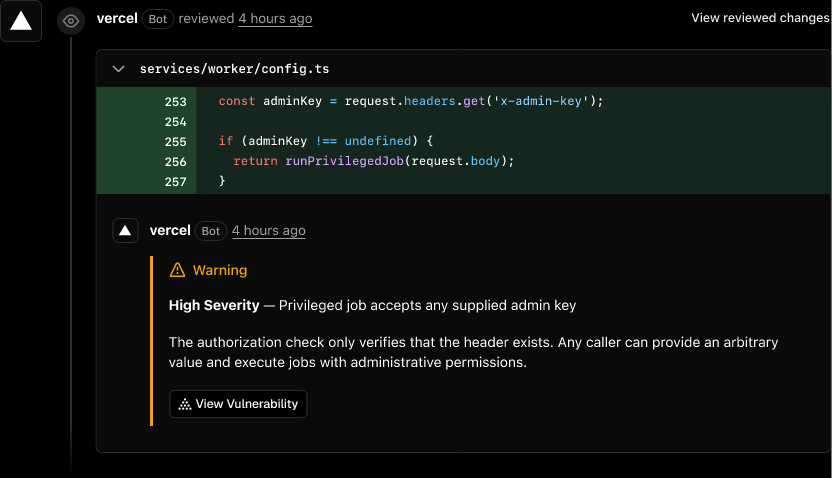
Vercel introduced Security Review on November 2, followed by its November 3 public-beta changelog. Available to Pro and Enterprise teams, it analyses changes pushed to connected GitHub repositories and presents findings in the Vercel dashboard and supported pull-request comments.
Review starts with a code change
The review uses project context and dependency information alongside the changed code. Teams can add plain-language policies, and monorepo reviews can be scoped to a project root. These features help focus analysis on the application being changed.
Context shapes the findings
An opt-in fixing agent proposes changes after examining a finding. The November 3 changelog describes fixes as pull requests requiring approval before merging. That explicit review boundary is important when generated changes alter authentication, authorisation or other sensitive application behaviour.
Fixes still require verification
The beta can make security feedback part of the existing development loop. Its practical value depends on finding actionable defects while limiting false positives and incorrect fixes. Teams can measure those outcomes against known issues and verify proposed changes through their usual code review and testing.
Image: Vercel / source announcement. Used for source-attributed editorial reporting; rights remain with the owner.
Sources & evidence
Sources describe the announcements and evidence available when this analysis was published. Company claims are attributed; plans and trials are not treated as sustained operation.