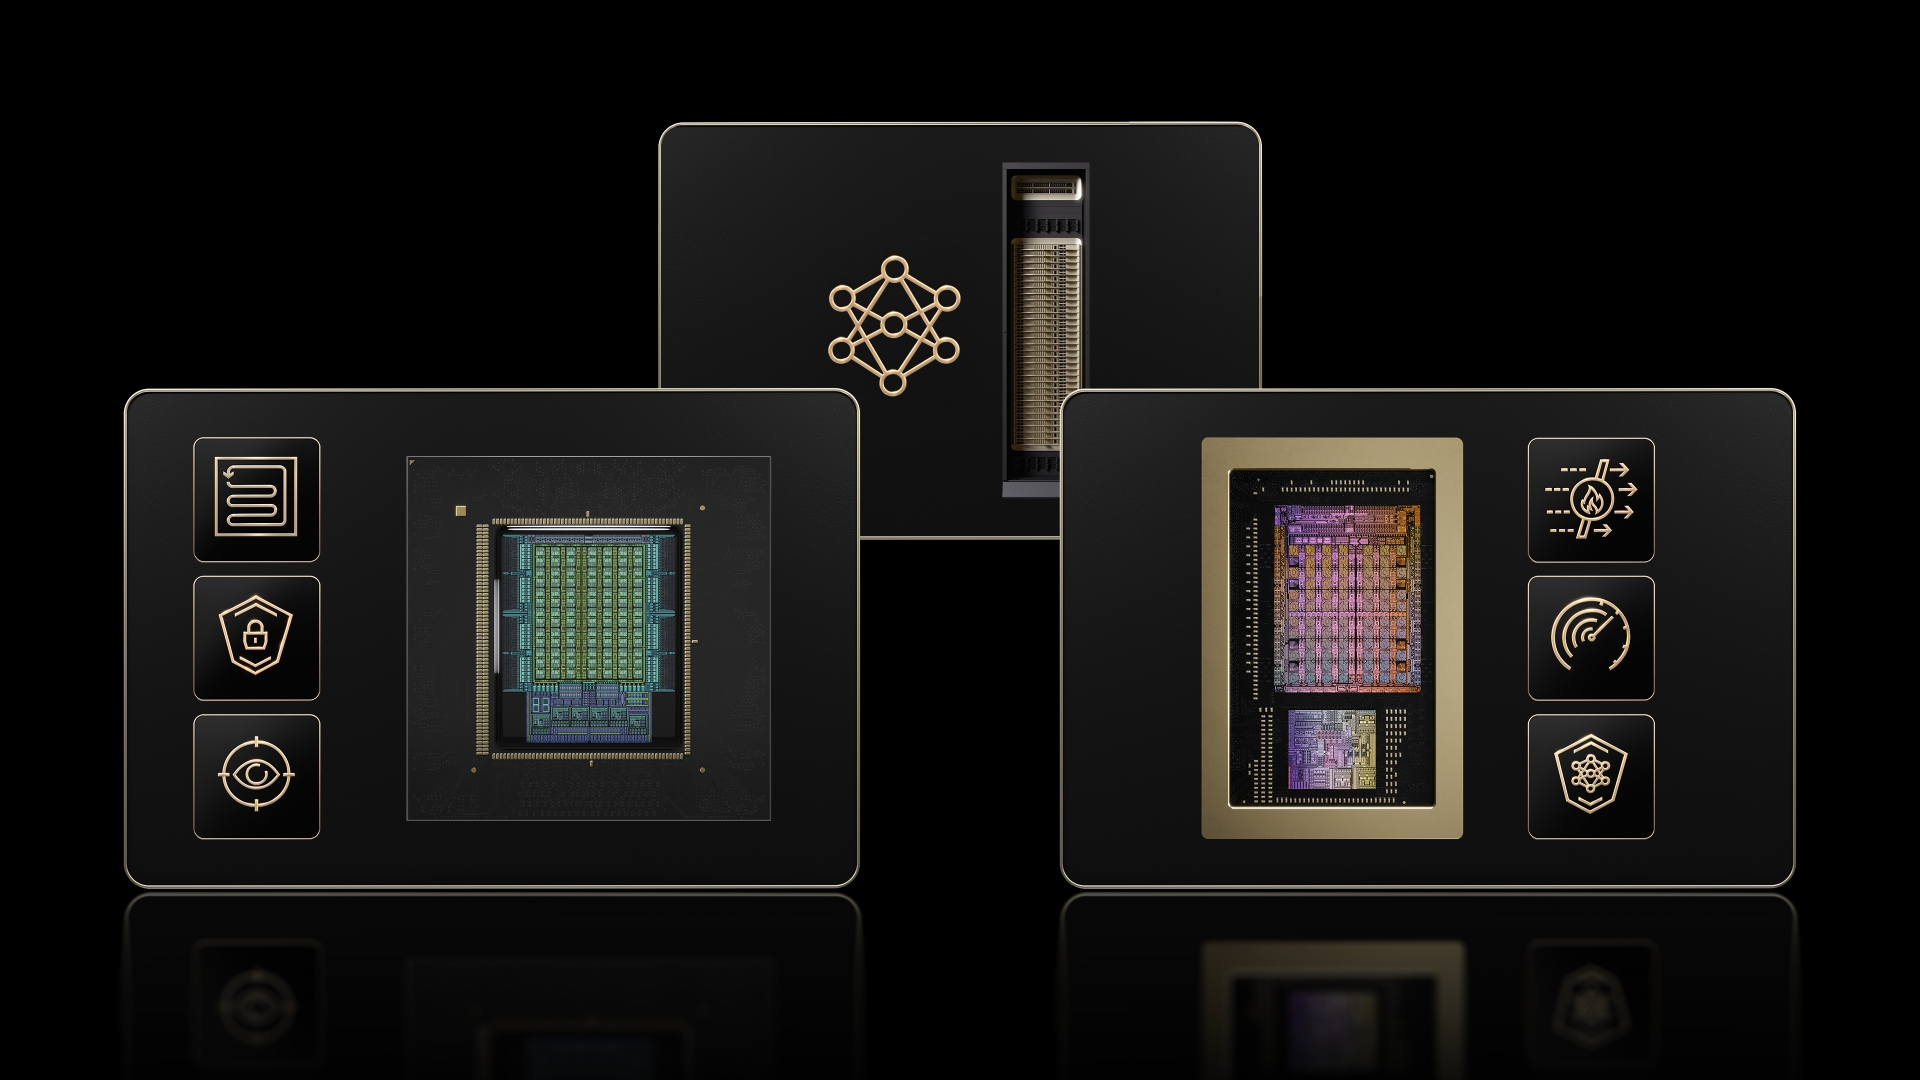
An agent’s promise to follow a rule is weaker than a system that can block a forbidden action. NVIDIA’s October 21 OpenShell reference architecture combines its secure runtime with Vera CPUs, Vera Rubin infrastructure and BlueField-4 DPUs running Sentry for out-of-band monitoring and policy enforcement.
Current impact
The immediate contribution is an architecture for separating agent execution from some of its controls. A reference design is not independent evidence that a deployed system resists every attack or that every integration exposes the same safeguards.
Potential greater impact
If organizations can enforce permissions outside the agent’s reasoning process, they could give useful automation access without relying only on prompts. The broader opportunity depends on policy completeness, identity propagation and enforcement across tools, files and networks.
What would establish progress
Validation should include attempted boundary violations and recovery after partial execution. Check which actions are blocked, what is logged and who can authorize exceptions. Hardware-backed enforcement can strengthen a boundary; it cannot decide whether the organization wrote the right policy in the first place.
Image: NVIDIA / official announcement. Used for source-attributed editorial reporting; rights remain with the owner.
Sources & evidence
Sources describe the announcements and evidence available when this analysis was published. Company claims are attributed; plans and trials are not treated as sustained operation.